Kubernetes deployments can lead to mismatched environments, particularly when secrets are synchronized at different times. Here’s how to tackle this issue effectively.
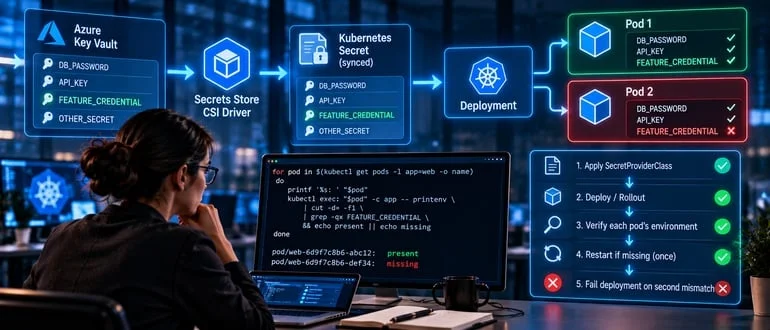
The complexity of managing secrets in Kubernetes environments often leads to discrepancies between running pods. A recently encountered scenario involved a deployment with two identical pods where one correctly integrated a Kubernetes Secret, while the other did not. This situation highlights the critical nuances of secret synchronization and environment variable initialization.
Identifying the Discrepancy
Upon inspection post-deployment, one of the two running pods revealed that it was missing an expected environment variable, despite both pods being designed to access the same secret resource. Utilizing the command:
for pod in $(kubectl get pods -l app=web -o name)
do
  printf '%s: ' "$pod"
  kubectl exec "$pod" -c app -- printenv \
    | cut -d= -f1 \
    | grep -qx FEATURE_CREDENTIAL \
    && echo present || echo missing
done
revealed one pod signaling "present" while the other showed "missing". This inconsistency warranted a deeper investigation into the secret synchronization process.
Synchronization Delays
The deployment utilized Azure Key Vault in conjunction with the Secrets Store CSI Driver, which introduced multiple timelines for updates. Each pod was configured to mount a CSI volume referencing a SecretProviderClass, which fetched values from the vault and subsequently mirrored them into a Kubernetes Secret. However, the synchronization process occurs after the pod mounts the provider class. Kubernetes, on the other hand, initializes environment variables at container creation. Hence, any updates to the secret do not affect currently running containers unless they are restarted.
Helm Chart Behavior
A postmortem analysis traced the problem back to how Helm managed the deployment order. In this case, Helm 4.2.3 executed the deployment and SecretProviderClass in a problematic sequence. Since Helm organizes resources based on their Kubernetes kind, the Deployment would be processed first, allowing a modification to the provider class to occur after the pods were already running. This results in a race condition where some pods may access an outdated version of the secret.
The Helm rendering verified that the states of the resources and observed pod activity supported this sequence of events, which ultimately led to the observed discrepancies.
Applying Changes to Static Workflows
In a different application scenario that involved using kubectl apply, a similar dependency issue emerged. As the deployment applied the provider class after rollout, this led to some pods not adopting the new secret until their environments were refreshed through a workload restart. This insight prompted a reordering of the application workflow, ensuring that the SecretProviderClass was applied before performing any rollouts. Such adjustments are pragmatic to avoid outdated configurations interfering with pod behavior.
Implementation of a Verification Gate
To fortify resilience against this kind of situation, a post-rollout verification mechanism was introduced. This gate checks each pod against the expected environment variables derived from the SecretProviderClass. The verification runs a second round of checks, and if mismatches persist, the gate triggers a deployment restart, thereby rectifying potential configuration issues that could affect application behavior.
Limitations of Current Health Checks
Health checks, which are intended to affirm application readiness, do not inspect for the presence of required environment variables tied to the latest version of a secret. Consequently, even when a health check returned a "200 OK" status, it did not ensure that all processes had received the necessary environment configurations, leading to an unsatisfactory state where some pods remained unresponsive to newer secret values.
Future Recommendations
To prevent similar discrepancies in Kubernetes secrets management, teams should consider applying or updating the SecretProviderClass prior to rollout. Moreover, implementing a thorough verification process that audits environment variables in each running pod serves as a solid approach to detect mismatches before they affect application performance. In scenarios where permissions for certain operations are limited, validating required variable names during application startup offers a way to ensure completeness and readiness of the deployment.
This enforced scrutiny not only enhances deployment reliability but also ensures that the overall system remains synchronized and responsive to configuration changes. In an environment where secrets play a pivotal role in application functionality and security, understanding and managing these complexities is essential for maintaining service integrity.



Discussion
Sign in to join the discussion.