IaC makes Kubernetes and hybrid infrastructure changes reviewable, helping teams use AI agents while keeping deployment approvals in human hands.
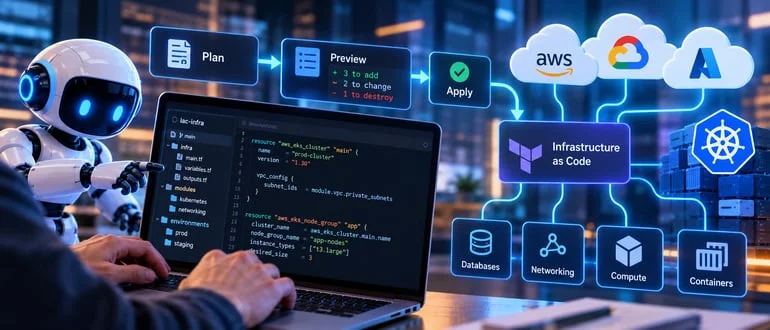
AI agents can already make changes through cloud provider interfaces. The harder question for platform teams is how to let them help without losing a clear view of what will change. Infrastructure as code (IaC) offers a practical boundary: agents can propose edits to versioned configuration, while teams preview and approve the resulting infrastructure changes before deployment.
That approach also addresses a less visible challenge: infrastructure keeps changing. Clusters need upgrades, databases and networks evolve, and workloads may rely on services that sit outside Kubernetes. IaC can bring these parts into a shared, reviewable workflow instead of treating initial provisioning as the whole job.
Infrastructure changes after provisioning
Provisioning cloud resources is only the start of infrastructure management. A Kubernetes cluster may be a prerequisite for shipping containerized applications, but it still needs maintenance. When a Kubernetes minor version leaves support, teams may face higher cloud costs unless they upgrade.
With IaC, teams describe infrastructure in code, including clusters, networking, databases and other resources. A proposed change can be previewed before deployment, giving engineers a way to inspect its likely effects. That matters for routine maintenance as well as for changes suggested by an AI agent: the configuration and its proposed impact stay visible for review.
Infrastructure as code is often discussed as a way to provision cloud resources. Its broader value is in managing infrastructure as it changes, with a record of the desired configuration and a process for applying updates.
Two models for managing cloud resources
Tools such as Crossplane, AWS Controllers for Kubernetes, Config Connector and Azure Service Operator use the Kubernetes Resource Model to manage cloud infrastructure. Their control plane runs inside a Kubernetes cluster, so teams need a cluster in place before using them to manage resources.
Pulumi, Terraform and OpenTofu take a different approach: they can describe a Kubernetes cluster alongside the applications and other infrastructure that depend on it. In this model, the cluster is one part of a larger system. A platform team can change a Kubernetes version in configuration, review a preview, and see which resources may be replaced instead of updated before approving deployment.
That visibility helps make upgrades easier to reason about. A version change may look small in code, but its operational consequences can be substantial if resources are recreated. A preview puts those consequences in front of the team before they reach the live environment.
External IaC tools can also let platform teams package infrastructure components as typed libraries. Application teams can then use those components without writing every low-level configuration themselves. This offers a way to provide shared platform capabilities while retaining defined boundaries around what teams can configure.
Managing dependencies beyond Kubernetes
Many Kubernetes environments depend on infrastructure that does not run inside the cluster. An external database is a straightforward example. IaC can manage that database alongside the cluster and application resources, with dependencies represented in the same program.
That can be useful when deployment order matters. Helm organizes chart manifests by resource kind, but that ordering does not express every dependency between resources. It also cannot wait for a resource that is not a Kubernetes object. IaC can describe those relationships across Kubernetes and external services, giving teams a way to coordinate their deployment.
The same model can help with hybrid and multi-environment setups. Teams can adjust configuration to provision a cluster in another region, deployment stage or cloud provider, while keeping their cloud-independent Kubernetes objects. The amount of work still depends on how provider-specific the configuration is, but managing infrastructure in code gives teams a common place to express and review those differences.
Teams also have choices about how drift is handled. An in-cluster control plane can automatically reconcile resources when actual state differs from the declared configuration. IaC workflows commonly present proposed corrections for approval first; automatic application can be enabled as a separate setting. That distinction gives platform teams control over whether drift triggers an immediate correction or a review step.
Giving agents bounded infrastructure work
Allowing an agent to make direct calls to cloud APIs gives it broad scope to create or modify resources. Because agents can produce inconsistent results, that access can make it difficult for operators to understand what changed and why, particularly across large environments.
Put an IaC program or stack configuration in the agent’s workflow and the task becomes more legible. The agent can propose a code change; a preview then shows what the configuration would do. Engineers can inspect the diff and approve it before deployment. The agent handles drafting and analysis, while the team retains the decision to apply the change.
This workflow doesn’t make an agent’s proposal correct by default. It does give reviewers a concrete artifact to assess and a view of the expected infrastructure effects. For teams evaluating agentic development, that review process can be more useful than granting an agent direct cloud access and trying to reconstruct its actions afterward.
Adoption can happen in stages
Most organizations won’t start with every resource described in one IaC program. Existing infrastructure can be imported into code incrementally. A preview with no proposed changes can confirm that the new configuration matches the current cloud state, providing a check before the team begins managing that resource through the new workflow.
IaC can also support teams beginning a Kubernetes migration from older systems. They can bring existing resources into the configuration as they progress, rather than needing to replace the whole environment before adopting code-based management.
Teams already committed to Kubernetes and GitOps can keep those operating habits. An operator can run IaC programs from inside a cluster, using a Kubernetes object that points to a Git branch. Kubernetes resources continue to be managed through the established model, while the operator runs the infrastructure program described by that object.
The practical choice is about where teams want infrastructure decisions to live and how they want changes approved. IaC can bring clusters, cloud resources and external dependencies into a versioned workflow, while giving AI agents room to prepare changes for human review. As agents take on more infrastructure work, the quality of the preview and approval process will matter as much as the agent’s ability to write the configuration.



Discussion
Sign in to join the discussion.